How Healthcare Leaders Can Build a Cybersecurity Culture
Healthcare leaders in India must build a proactive cybersecurity culture through leadership commitment, staff training, clear policies, and institutional governance to protect patient data and digital health systems.
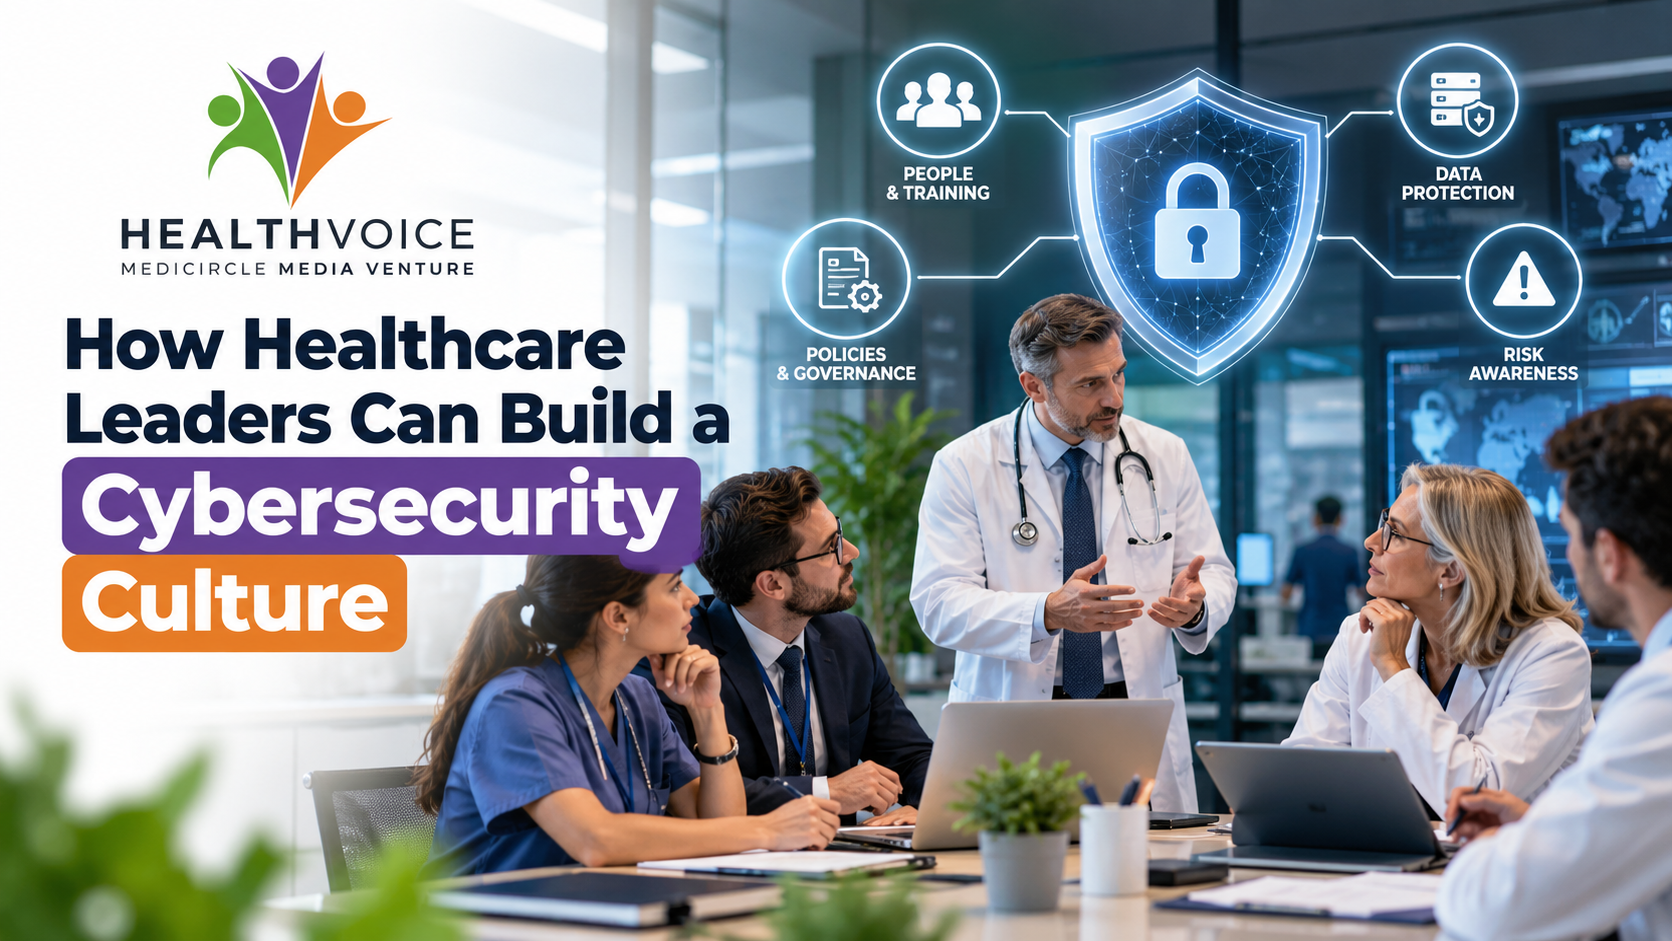
How Healthcare Leaders Can Build a Culture of Cybersecurity
Introduction
The digitization of India's healthcare ecosystem has brought transformative benefits, from telemedicine and electronic health records to AI-assisted diagnostics and the Ayushman Bharat Digital Mission. However, this rapid digital shift has also exposed hospitals, clinics, medical associations, and health networks to a growing and sophisticated range of cyber threats. Patient data breaches, ransomware attacks on hospital systems, and unauthorized access to medical records are no longer distant concerns limited to Western healthcare systems. They are happening in India today, and the consequences extend far beyond financial losses.
For healthcare leaders, whether they are hospital administrators, medical directors, CMOs, or heads of medical associations, cybersecurity can no longer be treated as an IT department responsibility alone. It must become a shared institutional value, embedded into the culture of every healthcare organization. Building that culture requires intentional leadership, consistent communication, and a clear understanding of why human behavior is often the greatest vulnerability in any digital system.
Understanding the Cybersecurity Threat Landscape in Indian Healthcare
India's healthcare sector is undergoing an unprecedented digital transformation. The Ayushman Bharat Digital Mission has enrolled hundreds of millions of citizens into a digital health ecosystem that connects hospitals, pharmacies, diagnostic labs, and insurers. While this integration creates extraordinary opportunities for care delivery, it also creates high-value targets for cybercriminals.
Several hospitals and health networks across India have already experienced ransomware attacks and data breaches in recent years. In 2022, the All India Institute of Medical Sciences in New Delhi suffered one of the most significant cyberattacks ever recorded in Indian healthcare, crippling hospital operations and exposing vulnerabilities in national health infrastructure. This incident was a serious wake-up call for healthcare leadership across the country.
The threat landscape includes:
- Ransomware attacks that lock critical hospital systems and demand payment for restoration
- Phishing attacks targeting doctors, nurses, and administrative staff through deceptive emails
- Insider threats arising from poor access controls or disgruntled employees
- Third-party vendor vulnerabilities through connected medical devices or software suppliers
- Unauthorized access to patient health records for insurance fraud or identity theft
Understanding that these threats exist is the first step. The second, and far more important step, is recognizing that technology alone cannot address them. Culture, leadership, and people must be part of the solution.
Why Healthcare Cybersecurity Requires a Cultural Shift
Most cybersecurity breaches in healthcare are not caused by sophisticated hacking techniques. They are caused by human error. A staff member clicks on a malicious link. A doctor uses a weak password. An administrative employee shares login credentials with a colleague. A vendor is given excessive access to sensitive systems. These are behavioral failures, not technological ones.
This is precisely why cybersecurity must be treated as a cultural issue rather than simply a technical one. When cybersecurity becomes embedded in organizational culture, staff at every level begin to think about data protection as part of their daily professional responsibilities. They ask questions before sharing information. They report suspicious activity without fear of blame. They follow protocols not because they are forced to, but because they understand the value of doing so.
For healthcare leaders, the challenge is to make this cultural shift happen in environments that are traditionally hierarchical, often understaffed, and frequently operating under clinical pressures that make procedural compliance feel burdensome. It requires both vision and practical execution.
Building Leadership Commitment as the Foundation
No cultural transformation in any organization succeeds without visible and sustained commitment from leadership. Healthcare leaders must demonstrate through their actions, not just their communications, that cybersecurity is a genuine institutional priority.
This means several things in practice. Leadership must allocate adequate budget for cybersecurity infrastructure, training, and third-party audits. It means that the CISO or cybersecurity lead must have a seat at the executive table and must be included in strategic planning conversations. It means that when a security incident occurs, leadership responds transparently and constructively rather than defensively.
Importantly, it also means that healthcare leaders must be educated themselves. Many senior leaders in Indian hospitals and medical institutions have deep clinical or administrative expertise but limited understanding of cybersecurity frameworks and threats. Investing in leadership-level cybersecurity literacy is not optional. It is foundational. When a CMO or hospital director understands the implications of a data breach, they are far more likely to champion the organizational changes needed to prevent one.
HealthVoice, as a platform connecting healthcare leaders and medical associations across India, has an important role in facilitating these conversations. Discussions about digital health governance, data ethics, and institutional cybersecurity preparedness are conversations that the medical community needs to have at scale.
Creating a Cybersecurity-Aware Workforce Through Continuous Training
One of the most effective investments a healthcare organization can make is in regular, relevant, and role-specific cybersecurity training. Generic training modules that staff are required to complete once a year are largely ineffective. What works is training that is contextual, frequent, practical, and tied to real-world scenarios that healthcare workers actually encounter.
Training programs should be designed with the specific workflows of doctors, nurses, administrative staff, billing teams, and IT personnel in mind. A radiologist needs to understand the risks of accessing imaging systems from personal devices. A front-desk staff member needs to know how to identify a social engineering call. A billing executive needs to recognize phishing attempts disguised as insurance correspondence.
Simulated phishing exercises, where the organization sends test phishing emails to staff and measures click rates, are a proven method for identifying vulnerabilities and reinforcing awareness without the consequences of a real attack. Organizations that run these simulations regularly see measurable improvement in staff behavior over time.
Leadership must ensure that training is not treated as a compliance checkbox. It must be presented as professional development with real career relevance, especially as India's digital health infrastructure expands and healthcare professionals are increasingly expected to operate within connected digital environments.
Establishing Clear Policies, Protocols, and Accountability Structures
A culture of cybersecurity cannot exist without clear, documented, and consistently enforced policies. Healthcare organizations need comprehensive policies that cover:
- Access control: who has access to which systems, data, and records, and why
- Password management: the use of strong, unique passwords and multi-factor authentication
- Device usage: guidelines on the use of personal devices for professional purposes
- Vendor and third-party access: how external partners access internal systems
- Incident reporting: clear and non-punitive channels for reporting suspected security incidents
In the Indian regulatory context, healthcare organizations must also align their policies with the Digital Personal Data Protection Act 2023, which places significant obligations on entities that process personal data, including health data. Compliance with ABDM data security standards is equally important for organizations participating in the national digital health ecosystem.
Accountability structures must be established clearly. Every staff member should know their responsibility in maintaining cybersecurity. This does not mean that the burden of security falls on individual employees. It means that everyone has a defined role in a broader institutional system.
Encouraging a Culture of Reporting Without Fear
One of the most damaging barriers to effective cybersecurity in any organization is the fear of reporting mistakes. When staff are afraid to admit they clicked on a suspicious link or accidentally shared sensitive information, incidents go unreported and small problems become catastrophic ones.
Healthcare leaders must actively work to create a psychologically safe environment where reporting a potential security incident is seen as a responsible and courageous act rather than an admission of failure. This requires consistent messaging from leadership, a clearly defined and accessible reporting process, and a demonstrated track record of responding to reports constructively rather than punitively.
Some of the most well-secured healthcare systems in the world operate on a no-blame reporting model for security incidents, similar to the no-blame culture that has transformed clinical safety in many leading hospitals. India's healthcare institutions can draw on this model and adapt it to local organizational cultures.
Integrating Cybersecurity Into Institutional Governance
Cybersecurity must eventually move beyond being a department-level function and become integrated into the broader governance framework of the healthcare institution. This means including cybersecurity risk in board-level risk registers, conducting regular third-party security audits, and ensuring that clinical technology adoption decisions include a security impact assessment.
Medical associations in India also have a critical role to play. Associations can develop and disseminate cybersecurity guidelines tailored for specific specialties, advocate for national standards in health data security, and create forums where healthcare leaders can share experiences and learn from one another. Platforms and communities that connect these leaders amplify the collective impact of individual organizational efforts.
Conclusion
Building a culture of cybersecurity in healthcare is not a single initiative or a one-time investment. It is an ongoing organizational commitment that requires leadership vision, human-centered training, clear accountability, open communication, and institutional governance. For India's healthcare sector, the stakes are especially high given the scale of digital health ambitions and the sensitivity of the data involved.
Healthcare leaders who take cybersecurity culture seriously today are not only protecting their organizations from financial and reputational harm. They are fulfilling a fundamental duty of care to their patients, their staff, and the wider community that trusts them with some of the most sensitive information in human life.
Frequently Asked Questions
Q1: What is the most common cause of cybersecurity breaches in Indian hospitals?
The most common cause is human error, including staff clicking on phishing emails, using weak passwords, and sharing login credentials. Technical vulnerabilities are a secondary factor. This is why training and awareness programs are as important as technology solutions.
Q2: How does the Digital Personal Data Protection Act 2023 affect healthcare organizations in India?
The Digital Personal Data Protection Act 2023 places legal obligations on healthcare organizations to protect the personal data they collect and process, including health records. Non-compliance can result in significant penalties. Healthcare institutions must establish data governance policies aligned with the Act.
Q3: What role does ABDM play in healthcare cybersecurity standards in India?
The Ayushman Bharat Digital Mission provides a framework for digital health data exchange that includes data security and privacy guidelines. Healthcare organizations participating in ABDM are expected to meet defined security standards to ensure the integrity and confidentiality of health records on the national platform.
Q4: How can small clinics and nursing homes in India improve cybersecurity with limited budgets?
Small healthcare facilities can start with basic but high-impact measures, including enabling multi-factor authentication on all systems, training staff to recognize phishing attempts, regularly updating software, using reputable cloud-based health management systems with built-in security, and engaging low-cost cybersecurity awareness programs.
Q5: Why should medical associations get involved in cybersecurity advocacy?
Medical associations represent large communities of doctors and healthcare institutions. They are uniquely positioned to develop specialty-specific cybersecurity guidelines, advocate for national policy standards, facilitate peer learning, and create awareness at scale. Their involvement can accelerate the cultural shift needed across the entire healthcare ecosystem.
Resources
- Ministry of Electronics and Information Technology (MeitY): Official source for the Digital Personal Data Protection Act 2023 and related digital governance frameworks in India.
- Ayushman Bharat Digital Mission (ABDM): Provides data security standards, interoperability guidelines, and digital health ecosystem policies relevant to all participating healthcare organizations.
- Indian Computer Emergency Response Team (CERT-In): India's national cybersecurity agency that issues advisories, guidelines, and incident response frameworks applicable to healthcare and other critical sectors.
- World Health Organization (WHO): Digital Health Publications: Offers global frameworks and best practice guidance on health data protection, digital health governance, and cybersecurity in healthcare systems.
- National Health Authority (NHA) India: Publishes operational guidelines and security frameworks for hospitals and health providers participating in digital health programs under the Government of India.
Interlinking Keywords
healthcare cybersecurity India, hospital data security, patient data privacy, digital health governance, ABDM data protection, medical data breach prevention, healthcare leadership training, clinical data protection, health information security, cybersecurity culture in hospitals
Last reviewed by:
Dr. Manthan Tripathi, HealthVoice Editorial and Medical Advisory Team, October 16, 2026.
Disclaimer
This article is intended for informational and educational purposes for healthcare leaders, medical professionals, and healthcare administrators. It does not constitute legal, regulatory, or technical cybersecurity advice. Organizations should consult qualified cybersecurity professionals, legal advisors, and relevant regulatory authorities before implementing any cybersecurity policy or data protection framework. HealthVoice does not assume liability for decisions made on the basis of information published in this article.
 Dr. Manthan Tripathi
#HealthcareCybersecurity #CybersecurityCulture